FutureIntelligence
No Result
View All Result
  • Login
  • Register
  • Home
  • Opinion
  • Radio & Podcasts
  • Events & Press
  • Tech Jobs
  • Reviews
  • About
FREE TO SUBSCRIBE
DONATE
  • Home
  • Opinion
  • Radio & Podcasts
  • Events & Press
  • Tech Jobs
  • Reviews
  • About
No Result
View All Result
FutureIntelligence
No Result
View All Result
Home Crime Computer Security

Heartbleed unlocks private keys and IDs

Jane Whyatt by Jane Whyatt
in Computer Security, Crime, Latest News, Something completely different, The technology we use and why
Reading Time: 2 mins read
A A
0
Heartbleed unlocks private keys and IDs
Share on FacebookShare on Twitter

The Heartbleed vulnerability has exposed users  to theft of ID and credit card details..
RELATED POSTS

University offers free cybersecurity training to bridge skills gap

Machine fools experts in tech milestone

LulzSec hackers jailed

Load More
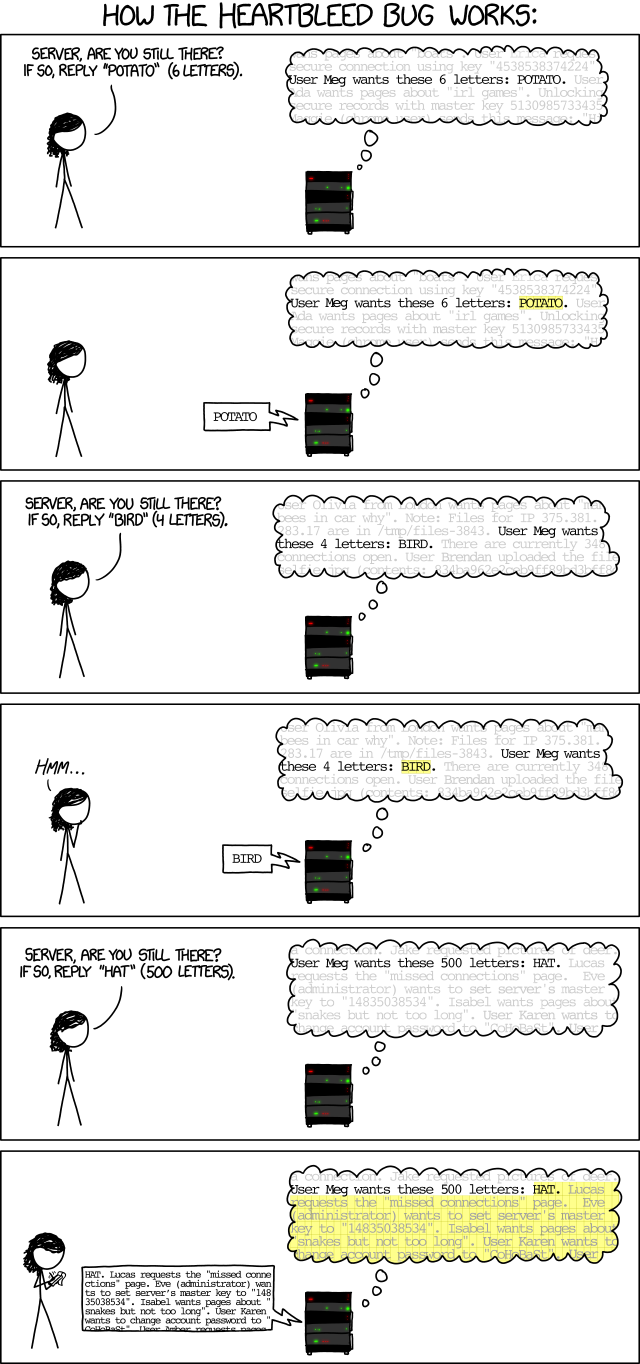
heartbleed_explanation
Heartbleed explanation from the web comic site www.xkcd.com

Parenting website Mumsnet, software company Oracle and the Canadian tax authorities are amongst the affected sites and users are advised to change their passwords. But Trend Micro’s Vice President for Security Research Rik Ferguson believes that is not necessarily good advice.

How to check for Heartbleed

Speaking on PassWord with Peter Warren, the tech radio show on London’s Resonance 104.4FM www.resonancefm.com/PassWord, Ferguson stressed that website owners should first check whether or not they are affected by the vulnerability, which arises out of faulty code in the Secure Software Layer (SSL) used to protect encrypted information. To check whether or not a server has the vulnerability he recommends that SMEs and bloggers should go to www.trendmicro.com/heartbleed and paste their URL into the testing page. If the test shows that Heartbleed is present, the server must be patched and the private keys revoked until the patch is in place, when new keys can be issued and users notified to change their passwords. Ferguson believes the vulnerability was not created deliberately but arose because of an oversight in Open Source SSL’s testing process. With only four staff – and offering a free product – Open Source SSL is under-resourced so it is not surprising that mistakes are made and go unnoticed.

Future Intelligence editor Peter Warren comments: “This is another example of bad code causing problems and further evidence that we need a new agency to oversee the quality of computer code. New software should be tested and registered before it is released, in the same way that the US Food and Drug Administration tests new drugs for safety.” 

https://futureintelligence.co.uk/wp-content/uploads/2014/04/Heartbleed-Rik-Ferguson-extract.mp3 https://futureintelligence.co.uk/wp-content/uploads/2014/04/Rik-Ferguson-Trend-Micro.mp3
advertise
ADVERTISEMENT
Tags: computer securityopen sourcepatchrtbleedSSlvulnerability
Previous Post

Robots switch from war to chores

Next Post

‘Humans first’ – report’s tech ethics call

Jane Whyatt

Jane Whyatt

Related Posts

University offers free cybersecurity training to bridge skills gap
Computer Security

University offers free cybersecurity training to bridge skills gap

With the modern world is increasingly dependent on smart technology, experts are becoming concerned with the alarming cyber security skills...

by peter
16th March 2017
Machine fools experts in tech milestone
Big data

Machine fools experts in tech milestone

An Artificial Intelligence has passed the Turing Test of imitating a human. The face of things to come - Eugene...

by Jane Whyatt
9th June 2014
Computer Security

LulzSec hackers jailed

Convicted hackers from the LulzSec splinter group of the Anonymous hacktivists' collective are now behind bars. Sentenced at London's Southwark...

by peter
18th May 2013
Computer Security

“Gary McKinnon was unlucky. He’s not even a very good hacker”

For the first time in 12 years, on the 16th of October, 2012, Gary McKinnon got lucky. McKinnon - 'virtual...

by Peter Warren
18th October 2012
Communications

The hunt for RBN the elite Russian cybercriminals

Last week in scenes reminiscent of a Cold War thriller, the Russian Business Network - a noted cyber crime group,...

by peter
15th November 2007
Next Post
Regulators snap at Snapchat

Regulators snap at Snapchat

Game Over – warning on botnets

Game Over - warning on botnets

Leave a Reply Cancel reply

Your email address will not be published. Required fields are marked *

This site uses Akismet to reduce spam. Learn how your comment data is processed.

Recent Posts

  • Europe’s digital War of Independence
  • Space cold war warms up
  • Digital ID card row: to be, or not to be

Categories

© 2021 Future Intelligence - Website by Kukoo Creative

Welcome Back!

Login to your account below

Forgotten Password? Sign Up

Create New Account!

Fill the forms bellow to register

*By registering into our website, you agree to the Terms & Conditions and Privacy Policy.
All fields are required. Log In

Retrieve your password

Please enter your username or email address to reset your password.

Log In
No Result
View All Result
  • Home
  • Opinion
  • Radio & Podcasts
  • Events & Press
  • Tech Jobs
  • Reviews
  • About

© 2021 Future Intelligence - Website by Kukoo Creative

This website uses cookies. By continuing to use this website you are giving consent to cookies being used. Visit our Privacy and Cookie Policy.
Are you sure want to unlock this post?
Unlock left : 0
Are you sure want to cancel subscription?