Millions of electronic hotel door locks including those of US President Donald Trump’s hotel group and other chains around the world have been found to be vulnerable to hackers.

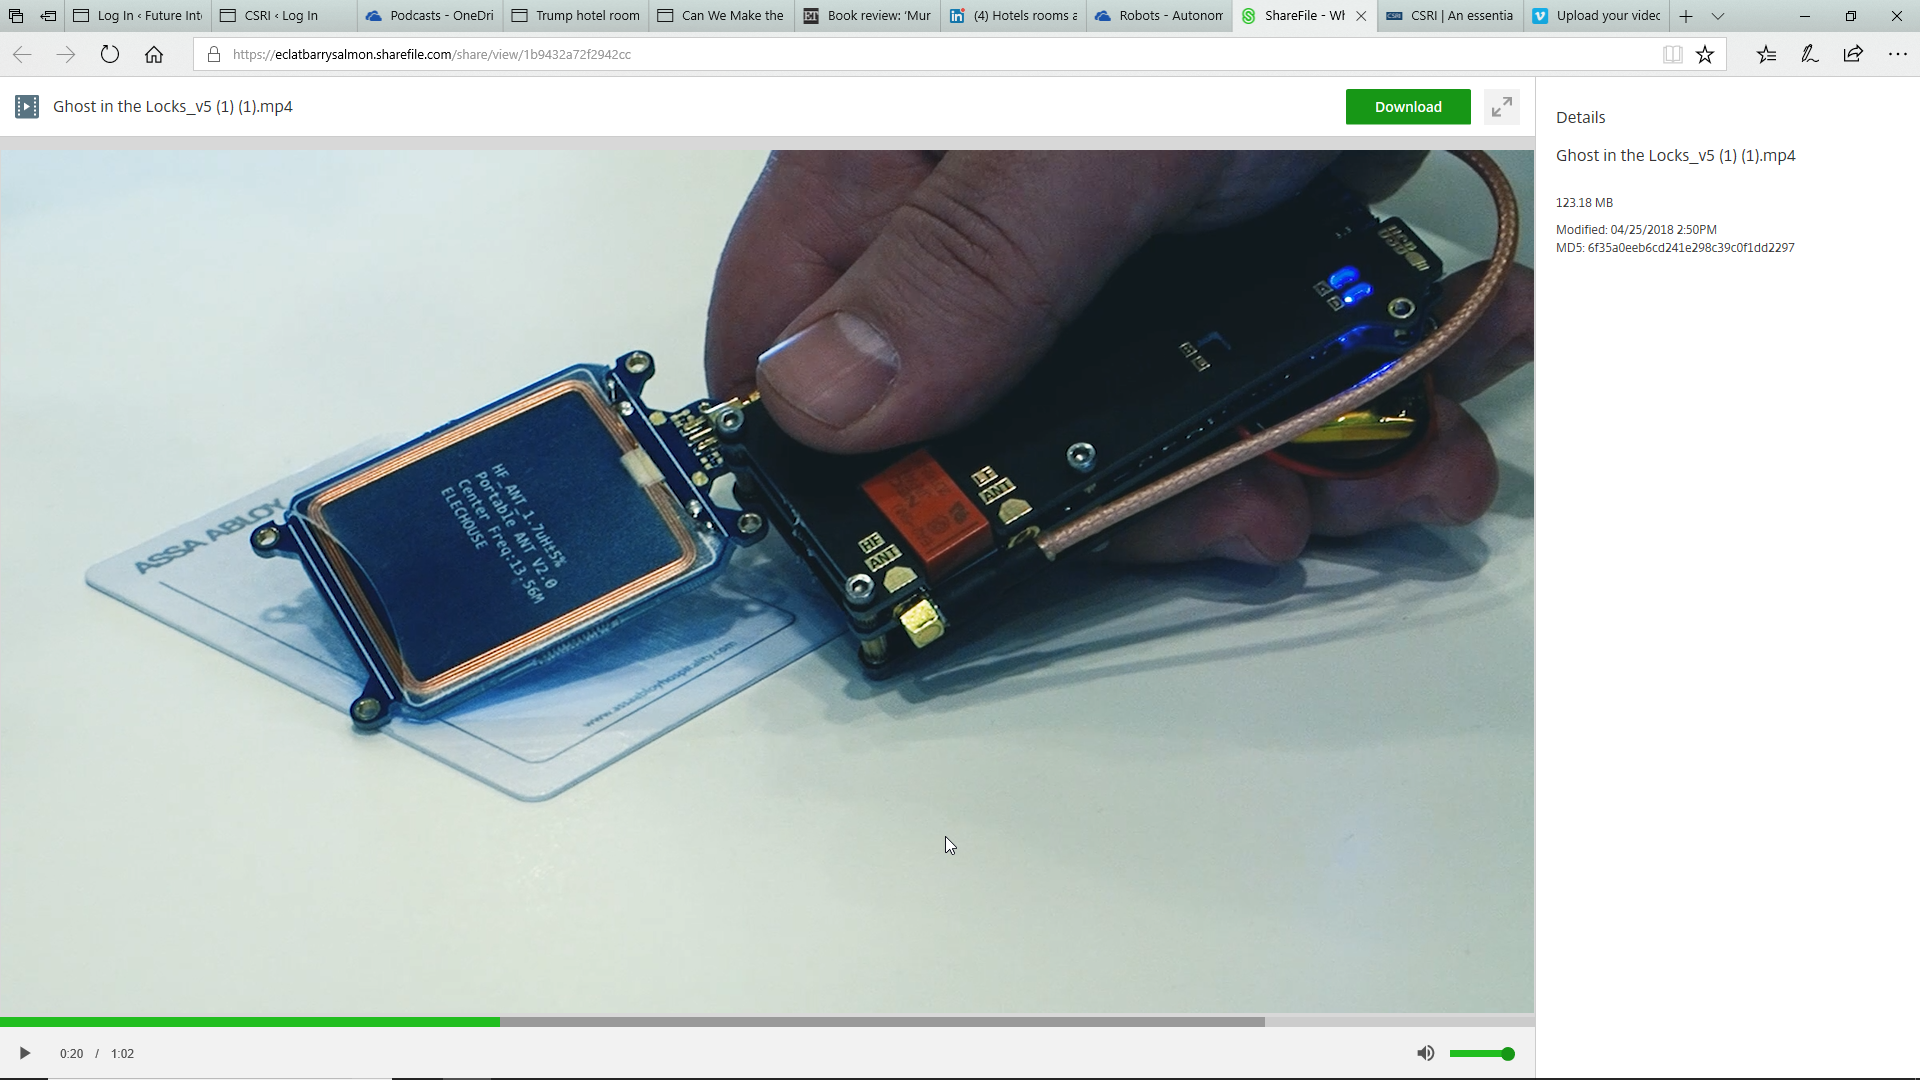
Using a simple technique to trap the ‘unique’ data from the ID cards produced by the Swedish company Assa Abloy, formerly known as Vingcard, ethical hackers from the Finnish company were able to show that they could effortlessly open hotel rooms, often from some distance away.
The experiment, demonstrated at a hacker’s convention in Florida on the 27th of April at 2.15pm, will cause panic in the security industry because the digital locks are not only used for hotel locks but also for room safes and even more importantly for the access systems to the secure rooms used by banks and technology companies to store sensitive customer data and account information.
The weakness in the door locking system has been circulating within the hacking community for a number of years and was almost certainly known about by the intelligence communities. One of the most disturbing points about the research is that NFC systems have now been rolled out in so many different parts of our lives and are now used in smart cards, clothes shops to create smart tags and in mobile phones – all prime targets for criminals and a signal to them to concentrate on research into the systems looking for weaknesses just as the researchers did.
Intelligence agents have long used hotel room penetration as a stock in trade for targeting foreign travellers and visiting delegations – a point underlined in the recent Channel 4 TV series ‘Deutschland 83’ which showed an East German Stasi undercover agent entering the hotel room of a member of a NATO delegation to steal information.
F-Secure researchers found that global hotel chains and hotels worldwide use an electronic lock system that can be exploited by an attacker to gain access to any room in the facility. The design flaws discovered in the lock system’s software, which is known as Vision by VingCard and used to secure millions of hotel rooms worldwide, have forced the world’s largest lock manufacturer, Assa Abloy, to issue software updates with security fixes to mitigate the issue.
The attackers using any ordinary electronic key to the target facility – even one that’s long expired, discarded, or used to access spaces such as a garage or closet.
Using information on the key, the researchers can create a master key with privileges to open any room in the building. The attack can be performed without being noticed.

Researchers say flaws they found in the equipment’s software meant they could create “master keys” that opened the rooms without leaving an activity log“You can imagine what a malicious person could do with the power to enter any hotel room, with a master key created basically out of thin air,” said Tomi Tuominen, Practice Leader at F-Secure Cyber Security Services. “We don’t know of anyone else performing this particular attack in the wild right now.”
The hackers targeted the hotel locks a decade ago after a colleague’s laptop was stolen from a hotel room during a security conference. When the researchers reported the theft, hotel staff dismissed their complaint given that there was not a single sign of forced entry, and no evidence of unauthorised access in the room entry logs.
The researchers decided to investigate the issue further, and to prove a point focused on the Vingcard system due to its reputation for quality and security.

“We wanted to find out if it’s possible to bypass the electronic lock without leaving a trace,” said Timo Hirvonen, Senior Security Consultant at F-Secure.
“Building a secure access control system is very difficult because there are so many things you need to get right. Only after we thoroughly understood how it was designed were we able to identify seemingly innocuous shortcomings. We creatively combined these shortcomings to come up with a method for creating master keys.”
“These security oversights were not obvious holes. It took a thorough understanding of the whole system’s design to identify small flaws that, when combined, produced the attack. The research took several thousand hours and was done on an on-and-off basis and involved considerable amounts of trial and error.”
F-Secure has notified Assa Abloy of the findings and has collaborated with the lockmaker over the past year to implement software fixes. Updates have been made available to affected properties.